XBOW safely proves what is exploitable on your running web applications and APIs. It avoids any action that could cause data loss or downtime. You decide what XBOW tests and how far it goes, and XBOW logs every action.
Four Principles Govern Every Assessment
Demonstrate, don't weaponize
XBOW proves each exploit safely and goes no further than the impact level you set.
Protect customer data
XBOW does not use your data for model training without express permission.
Stay in scope
Testing stays on the systems and domains you authorize. Everything else is off-limits.
Minimize disruption
XBOW avoids any action that could cause data loss, corruption, or downtime.
Set the Right Controls
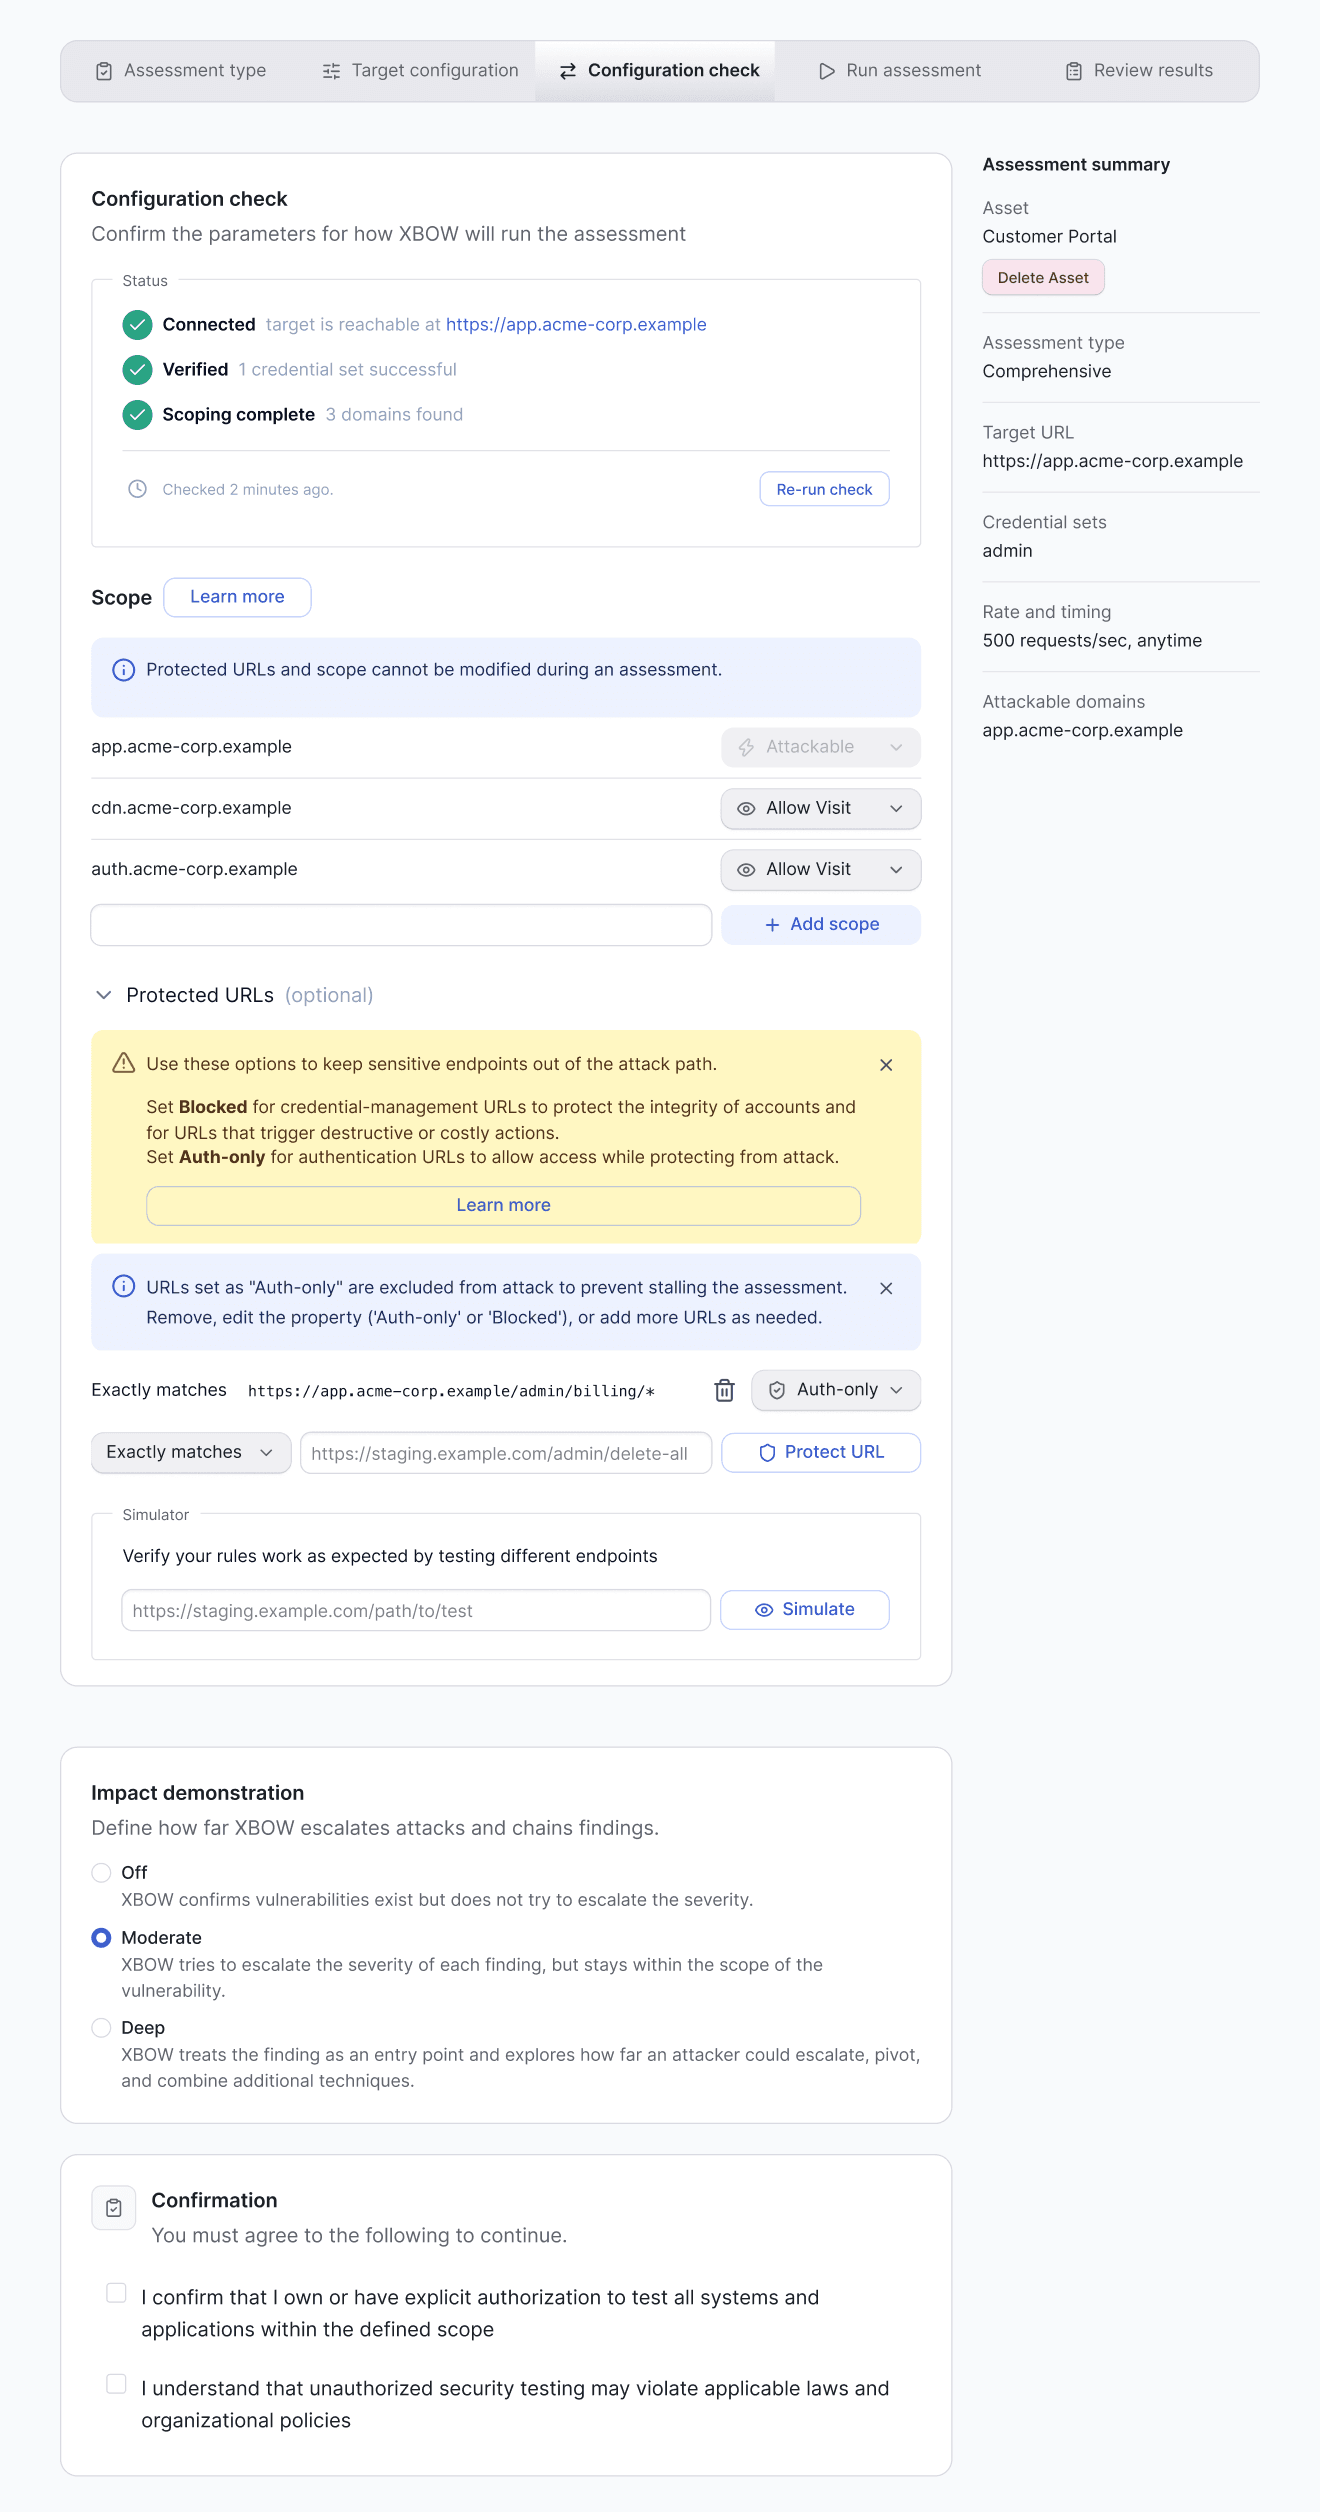
Before an assessment starts, XBOW maps the domains your asset uses and flags URLs that could disrupt testing. You review that setup and add your own limits.
XBOW marks first-party domains as attackable and third-party domains as visit-only. Change any designation and add domains it missed.
Mark sensitive URLs as auth-only or blocked, on top of the ones XBOW protects for you.
Choose how far XBOW goes after it confirms a finding, from no escalation to escalating across vulnerability classes and systems.
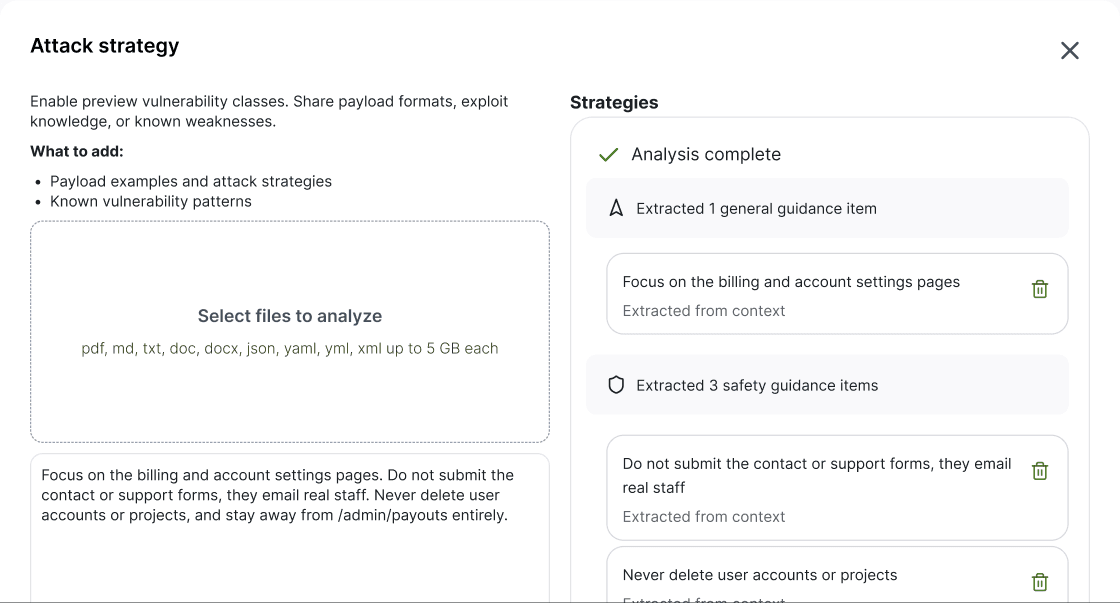
Tell XBOW what to avoid in plain language. The safety model applies it to every action before it runs.
Built on Proven Safety Layers
XBOW enforces safety in independent layers. Any one layer can stop an unsafe action.
A safety model on every command
A separate safety model reviews each command before it runs, so no agent can override the check. It blocks destructive operations, credential changes, session disruption, out-of-scope activity, control evasion, data exfiltration, and anything you prohibit in the assessment settings.
Read the blogFixed rules
Deterministic checks block known destructive patterns without relying on any model's judgment.
Network boundaries
Traffic goes only to authorized destinations. XBOW's own infrastructure and internal addresses are off-limits.
Proof without damage
XBOW proves vulnerabilities with benign techniques. For a SQL injection, that means a one-time delay.
Automatic stops
XBOW pauses when your target becomes unhealthy and resumes when it recovers. It shuts down any agent that keeps proposing blocked actions.
Standing directives
As a backup to the hard controls, every agent follows instructions that override anything else, including text on your target written to manipulate it.
Bring your risk review questions to the demo. We'll walk through the controls in the console.
Get a demoGovernance and Visibility
XBOW records every assessment step, so your team and your auditors can review what happened.
Full traces
See each action the agents took, the reasoning behind it, and the commands they ran.
Request and endpoint logs
See every request XBOW sent, with time, method, URL, and status code, and every endpoint it tested.
Audit log
Administrators see configuration changes and security events for the organization.
Roles, SSO, and SCIM
Assign roles, sign in through your identity provider, and provision users from it.
Data protection
XBOW encrypts data at rest with AES-256 and in transit with TLS 1.2 or 1.3 for API and Console traffic.
Compliance
XBOW is GDPR, SOC 2 Type 1, SOC 2 Type 2, and HIPAA compliant.
- GDPR
- SOC 2 Type 1
- SOC 2 Type 2
- HIPAA
Store security-sensitive data in Australia, Canada, Europe, Japan, or Singapore.
- Australia
- Canada
- Europe
- Japan
- Singapore