XBOW is an autonomous offensive security platform for your applications and APIs. It discovers, chains, and exploits vulnerabilities with the depth of the best human attacker, proves every finding with a working exploit, and re-tests every fix.
From context to confirmed exploit.
XBOW runs the whole assessment autonomously, continuously, or on demand, every time your applications change.
Point XBOW at a target and give it context: docs, credentials, API specs, architecture notes, source code. XBOW can run without context, but the more context it has, the deeper it goes.
XBOW builds a live map of the target: applications, endpoints, parameters, auth flows. In one engagement, it found 530 endpoints where the team expected 15 to 30.
A coordinator decides what to test, where, and in what order, then directs thousands of agents across the target.
Agents attack in parallel. They reason through and chain vulnerabilities with an extensive offensive toolkit. They exploit paths scanners never find.
Independent validators confirm each exploit is reproducible. Findings in generally available classes are confirmed deterministically; preview classes are labeled.
Once your team deploys the fix, XBOW re-tests it and confirms the issue is closed.
An autonomous extension of your offensive team.
Set the rules. XBOW operates within them.
Fully autonomous attacks.
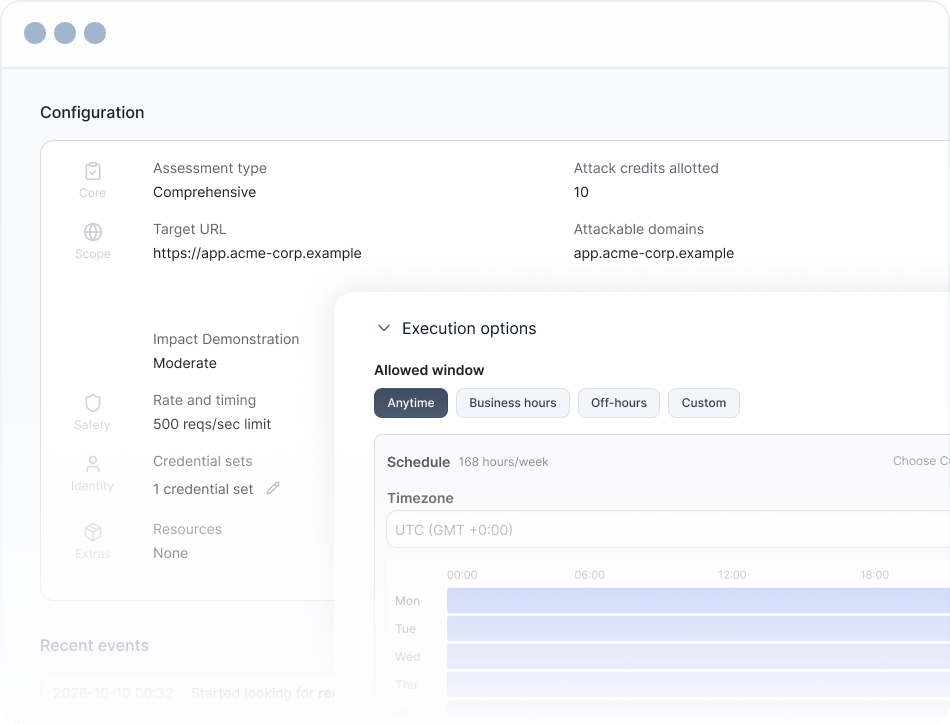
You set the scope, the impact level, and the testing window. Every action is logged, and findings are reviewed before you see them. Want a human to approve the first run? Start there.
Define the scope.
Control what XBOW can and cannot test. XBOW operates within the scope you set, with protected URLs and allowlisted paths filled in automatically.
Choose impact level.
Off, moderate, or deep. Rate limits, testing windows, and one-session-at-a-time mode keep load where you want it.
Proof without damage.
Production-safe checks prove exploitability without modifying data or disrupting systems. A safety judge reviews every action before execution, command checker blocks destructive behavior.
Observable and auditable.
Every action is logged and reviewable. Tag XBOW's traffic with custom headers so your team can track easily. Pause at any time.
Board and auditor-ready reporting.
Clear evidence, severity, and remediation in reports your board and auditors can trust, with the full trace behind each finding.
Start where comfortable.
Start with unauthenticated external testing. Move on to one targeted run, then authenticated. Or start with a small run on a low-risk application. Most teams reach production within the proof of value.
Open a finding. See the full attack flow.
Every finding is a complete, reproducible trace: the chained attack path, the working exploit, and a full log of every decision and tactic the agents took. Nothing hides behind a severity score. Review the whole chain.
Every application you expose. Not just the crown jewels.
Portfolio-wide testing.
Test your full external application footprint from the internet, the way most attackers do it. A Fortune 50 organization assessed 180 applications in a month, reaching full coverage.
What it takes to get there.
Testing every application depends on three things: credentials that work, network access, and a target list. XBOW's onboarding team helps with all three, including sorting thousands of URLs down to the real targets before you size anything.
What XBOW tests.
Web applications and APIs, authenticated and unauthenticated, in production or staging.
Embed XBOW in your pipeline.
Your applications and APIs change every day. The XBOW API launches assessments programmatically and at scale, across every application and endpoint you expose, on your own release cadence. Pull findings into Jira, GitHub issues, or the coding agents your team already runs.
Frontier models find vulnerabilities. XBOW proves them.
Frontier models are remarkable at finding possible vulnerabilities. But an LLM is not an offensive security platform. XBOW proves exploitability, stays safe in production, covers every application, orchestrates thousands of agents, controls cost, routes across models, and earns your auditors' trust.
No frozen model.
There is no permanent best model. Different models lead at recon, code understanding, exploitation and chaining, and the ranking changes every few months. XBOW benchmarks them, routes each task to the current best, and swaps when the frontier moves. A vendor that fine-tunes one model has handed you a snapshot.
Proof, not a flood of maybes.
The harness validates each finding with a working exploit, so model output becomes proven risk.
Safe and governed by design.
Non-destructive execution, audit trails, and rigorous validation before findings surface.
Orchestration at scale.
Coordinate agents across every application without duplicated work or lost coverage, across your entire portfolio.
Deployment and compliance.
Data separation, residency, and compliance aligned to your requirements.
- SOC 2
- ISO 27001
- ISO 42001
- PCI DSS
- NIS 2
- HIPAA
- GDPR
Supports 40+ frameworks.