XBOW maps your external footprint, shows where PHP appears to be in use, and points you to the assets worth testing first. Delivered by an XBOW engineer, at no cost, and only after we confirm scope with you.
Why now
Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, were patched on 21 October and are already being probed. Patching is the first move. The harder question is where PHP is actually running across everything you own, because that is rarely on one list.
A free perimeter assessment answers that question for you, and gives you a short, prioritized view of where to look first.
What you get
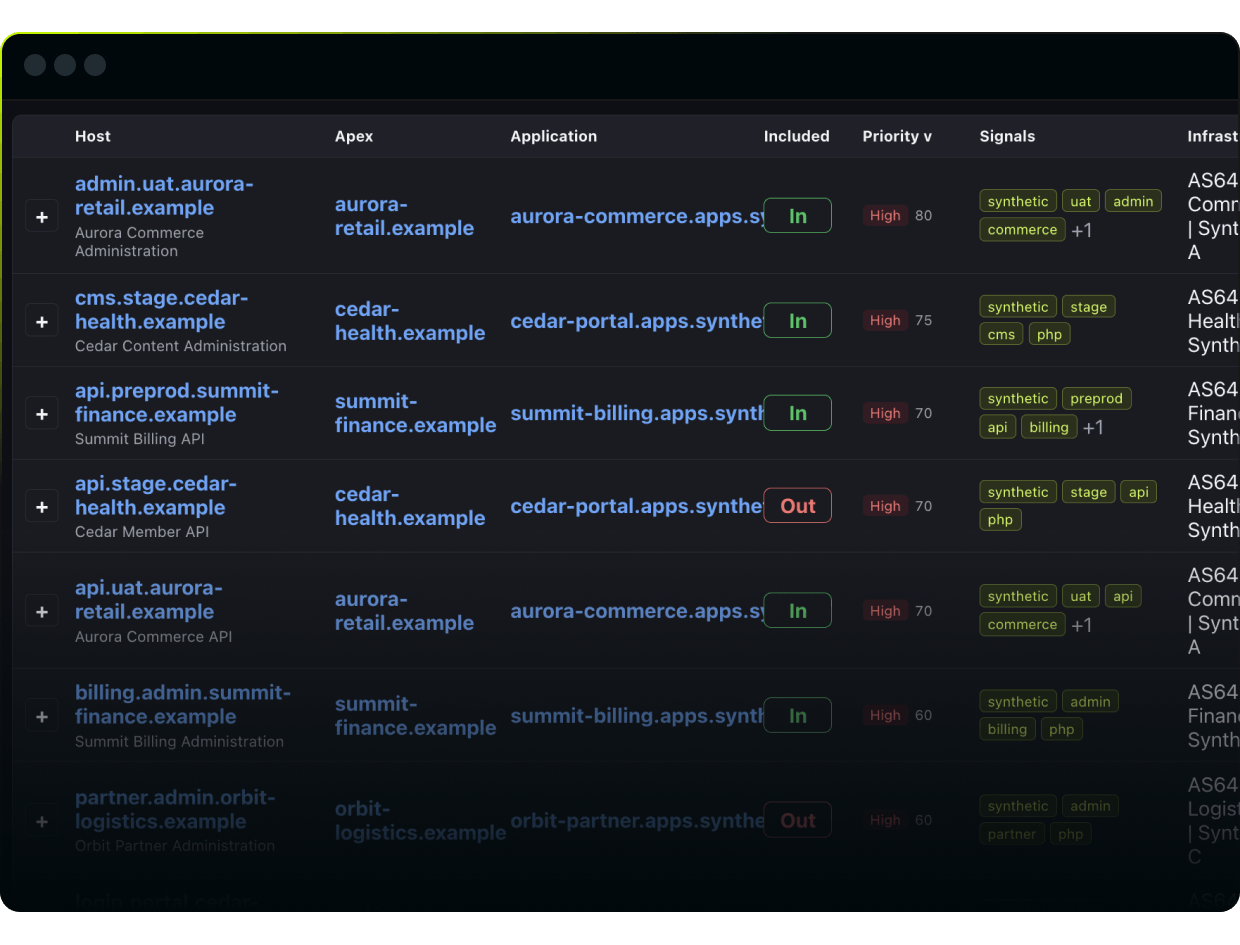
Your external footprint, mapped
We identify the domains and subdomains associated with your organization and how many are live and reachable, so you can see the shape of what is exposed.
Where PHP shows up
We flag where PHP appears to be in use across that footprint, so you can focus your patching and testing where it matters.
A prioritized shortlist
Not a raw dump. A ranked view of the assets with the most to look at, in a report you can share with your team and your leadership.
A conversation, not just a file
An XBOW engineer walks you through what we found and what we would test next, so you leave with a plan rather than a spreadsheet.
How it works
You request it
Fill in the short form below, including the domains you want us to look at, and confirm you are authorized to ask for this.
We confirm scope with you
A member of our team contacts you to confirm who you are, which domains are in scope, and that we have your consent. Nothing runs before this conversation.
We run the assessment
An XBOW engineer maps the footprint and prepares your report. For large organizations with many subsidiaries, we agree the scope with you first.
We walk you through it
We share the report, talk through the priorities, and, if it is useful, discuss a deeper evaluation under a standard agreement.
How it works
You request it
Fill in the short form below, including the domains you want us to look at, and confirm you are authorized to ask for this.
We confirm scope with you
A member of our team contacts you to confirm who you are, which domains are in scope, and that we have your consent. Nothing runs before this conversation.
We run the assessment
An XBOW engineer maps the footprint and prepares your report. For large organizations with many subsidiaries, we agree the scope with you first.
We walk you through it
We share the report, talk through the priorities, and, if it is useful, discuss a deeper evaluation under a standard agreement.
Who this is for
Security and engineering leaders who want a fast, outside-in read on where PHP sits in their attack surface, without standing up a project to find out. There is no cost and no obligation. If a deeper test makes sense afterwards, we will tell you what that looks like.